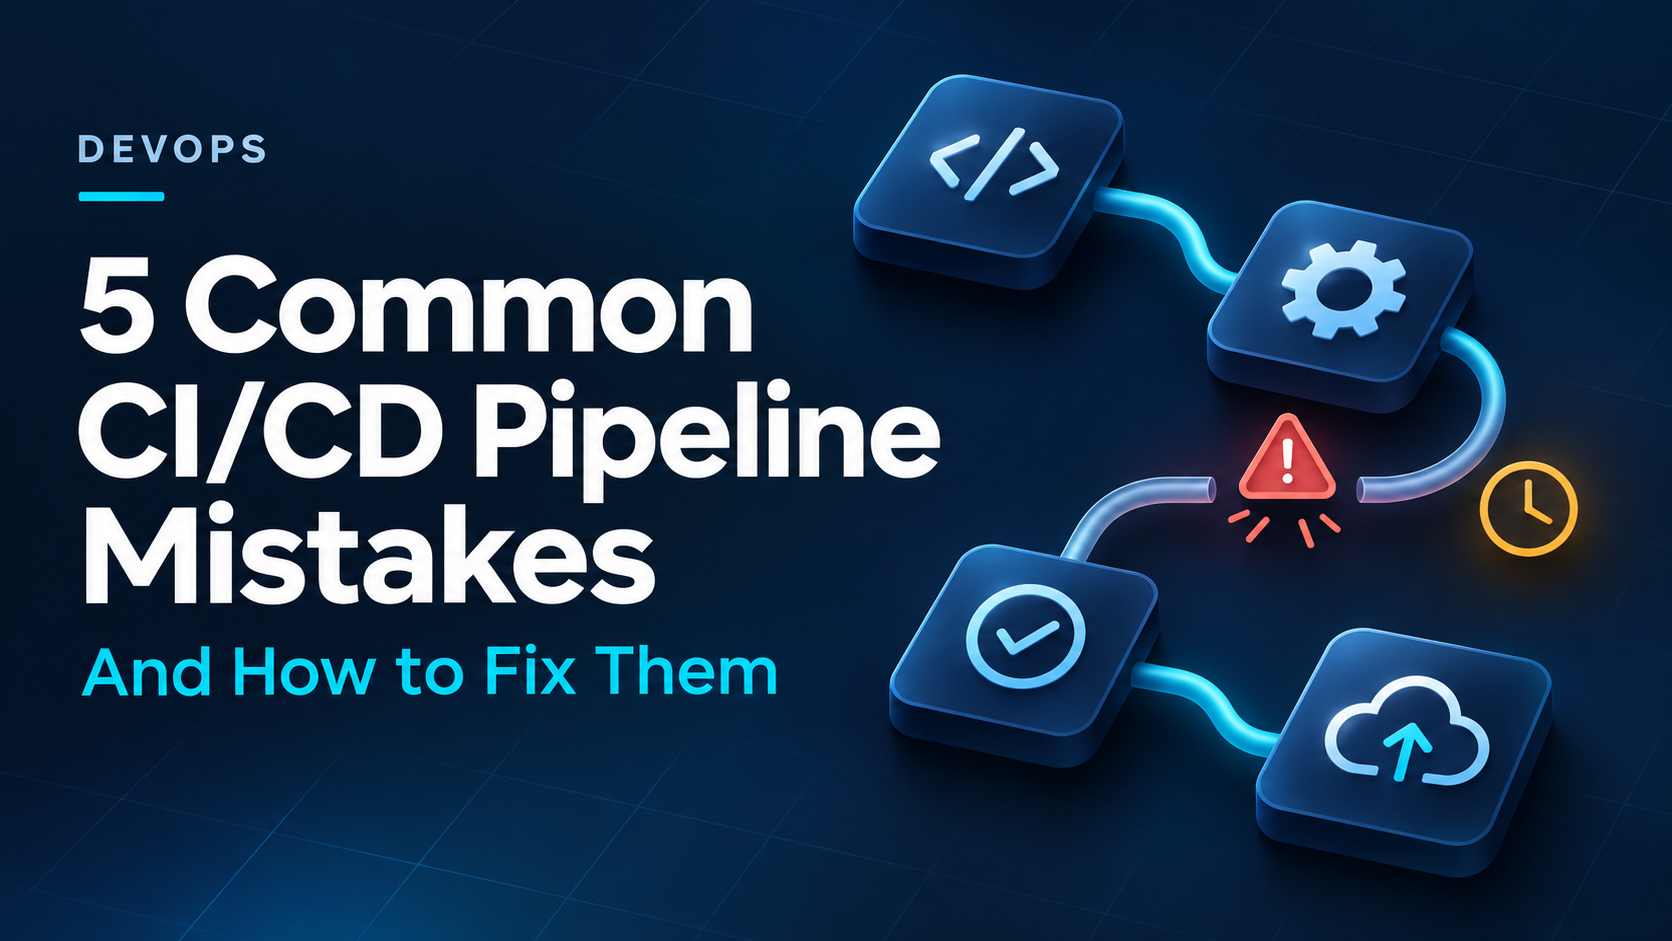
CI/CD pipeline mistakes can slow software delivery even when teams have automated their builds, tests, and deployments. Long waiting times, unreliable test results, inconsistent environments, and weak security controls make updates harder to release with confidence.
CI/CD connects the steps involved in preparing software for release. Continuous integration checks changes as developers combine their code. Continuous delivery keeps tested changes ready for release, while continuous deployment releases changes automatically after they pass the required checks.
Automation helps, but the process still needs attention. These five common mistakes explain why CI/CD pipelines become slow or unreliable and what teams can do to improve them.
1. Not Monitoring CI/CD Pipeline Performance
A pipeline that worked well when an application was small may struggle as it grows. Teams add tests, security checks, and build steps over time. Each addition takes time and resources, but its effect on the overall process can go unnoticed.
A slow pipeline does not always mean the code takes longer to build. Jobs may wait for an available machine, spend time downloading files, or run with too few resources. Looking only at the final completion time makes these problems difficult to tell apart.
Start by measuring where the time goes. Track the duration of individual steps, how often they fail, and how long jobs wait before starting. Compare results over several runs to separate a recurring problem from an occasional delay.
Give someone responsibility for reviewing pipeline performance. If testing becomes slower, investigate the tests. If jobs spend longer waiting, review available computing resources. Knowing the source of a delay makes it easier to choose a useful fix.
2. Ignoring Flaky Tests and Unreliable Results
A flaky test passes in one run and fails in another, even though the code has not changed. These inconsistent results make it difficult to decide whether the application has a defect or the test itself needs attention.
For example, a test may expect a page to load within a fixed number of seconds. It passes on a fast machine but fails when the testing environment is busy. Running it again may produce a passing result without explaining the original failure.
Repeated retries can weaken trust in automated testing. If developers expect failures to disappear on their own, they may overlook a real problem.
Investigate tests that fail inconsistently. Check whether they rely on timing, shared data, or an external service that is sometimes unavailable. Each test should have the data and conditions it needs without depending unnecessarily on another test.
Assign recurring issues to an owner. If a test is temporarily removed from release checks, keep investigating it and set a repair deadline. A passing pipeline is less useful if important tests have simply been switched off.
3. Running Every Check in One Long Sequence
A pipeline can include the right checks and still make people wait unnecessarily. This happens when every step runs after the previous one, even though some checks could happen at the same time.
Think of reviewing a document. One person can check spelling while another checks the facts. Making the second reviewer wait does not necessarily improve the result. Independent software checks can work in a similar way.
Review which steps need results from earlier stages and which can run separately. Running independent checks together, known as parallel execution, can reduce waiting time when enough computing resources are available.
The checks should also match the change being made. A documentation update may need different validation from a change to how customers sign in. Teams should make these decisions carefully, keeping the testing needed to catch defects.
Focus on the steps that determine the total waiting time. Making a quick task faster will have little effect if another required task still takes much longer.
4. Using Inconsistent Build Environments and Dependencies
An application may work on a developer’s computer but fail during automated testing. The difference can come from the environment used to build or run it.
An environment includes software tools, settings, and system components. If developers and the pipeline use different versions, the same code may behave differently. Dependencies, the external software packages an application uses, can introduce similar problems when their versions change unexpectedly.
Keep development and build environments consistent wherever practical. Record tool versions, settings, and dependencies so the team can recreate the setup when a failure needs investigation. This makes it easier to understand what changed between a successful run and a failed one.
Plan updates and test them before adopting them across the team. Consistency should not mean leaving old software untouched indefinitely.
Reusing downloaded files can reduce setup time, but saved files should not be the only reason a build succeeds. The pipeline should also work when it starts with a clean environment.
5. Overlooking CI/CD Pipeline Security
CI/CD pipelines often have access to source code, testing systems, and production environments. Without clear limits, a routine job may receive far more access than it needs.
Passwords stored in project files, access keys exposed in logs, and unrestricted deployment permissions all create avoidable risks. External software packages can also contain security weaknesses that reach the application through the build process.
Treat access as something each job must need. A job that checks code should not automatically have permission to release changes to production. Store sensitive credentials in protected systems and keep them out of source files and visible logs.
Include security checks for dependencies and build environments. Review who can approve releases and which changes are allowed to reach production.
If a credential is exposed, replace it promptly. Deleting it from a file does not stop someone from using a copy. Assign responsibility for reviewing security findings so problems do not remain unresolved between releases.
How to Review Your CI/CD Pipeline Health
Start with recent pipeline runs. Look for steps that regularly take the longest, tests that pass only after retries, and jobs that spend time waiting to start. These patterns provide a clearer picture than one unusually slow or unsuccessful run.
Next, check whether the team can reproduce the build environment and explain who has deployment access. Record unanswered questions as review tasks. Prioritise issues that repeatedly delay work, weaken testing, or expose systems to unnecessary risk.
How Nikqik Technologies Supports Reliable Software Delivery
Nikqik Technologies’ Quality Assurance services support software testing and validation, while Cloud Consulting helps teams review the infrastructure and environments their applications depend on.
Application Development supports maintainable software and consistent development practices. Managed Services supports ongoing monitoring and maintenance as systems and workloads change. These service areas connect the quality of the application with the reliability of the systems supporting it.
Explore Nikqik Technologies’ IT services or connect with our team to discuss your software delivery challenges.
Keep Your CI/CD Pipeline Reliable
CI/CD best practices work when teams apply them consistently. Review performance, investigate unreliable tests, maintain predictable environments, and control access throughout the delivery process.
Start with one recurring problem from recent pipeline runs. Assign an owner, make a focused change, and compare the results. Use that evidence to decide what needs attention next.